“The question is no longer whether AI will touch your transaction layer. It already has — at your bank, your payment processor, your ERP vendor. The question is whether you’re the one directing it.”
The Control Problem at Scale
Most finance leaders don’t have a data problem. They have a signal problem.
General ledgers at mid-market and enterprise organisations now process anywhere from tens of thousands to tens of millions of transactions per period. The volume is not the challenge — modern ERP systems handle volume well. The challenge is that somewhere inside that volume, on any given day, there are mis-postings, duplicate payments, policy violations, and early-stage fraud patterns that no human review cadence can reliably surface in time to matter.
Traditional controls — three-way matching, segregation of duties, monthly reconciliations, periodic internal audits — were designed for a transaction environment that no longer exists. They catch errors in arrears. They sample rather than sweep and they depend on the assumption that material issues will surface through exception reports designed to find the errors you already know to look for.
AI-driven transaction monitoring breaks from that assumption entirely. It monitors continuously, learns what “normal” looks like for your specific organisation, and surfaces anomalies that no pre-written rule would have caught.
Table 1 — Pipeline comparison: Traditional batch processing vs. AI-driven continuous processing
| Dimension | Traditional processing | AI-driven processing |
| Invoice intake | Batch, end of week | Any format, any time, real-time |
| Data entry | Manual keying, ~3–5 min per invoice | AI extraction <30 seconds, 95%+ STP |
| Reconciliation | Month-end, periodic | Continuous, near real-time |
| Error detection | 15–30 days average lag | Minutes to hours |
| Audit coverage | ~5–10% sample | 100% of transactions |
Table. 1 — The control gap in traditional processing — the time between a transaction occurring and an error being detected — is the core problem AI addresses.
What AI Is Actually Doing in the Transaction Layer
Automated Capture and Classification
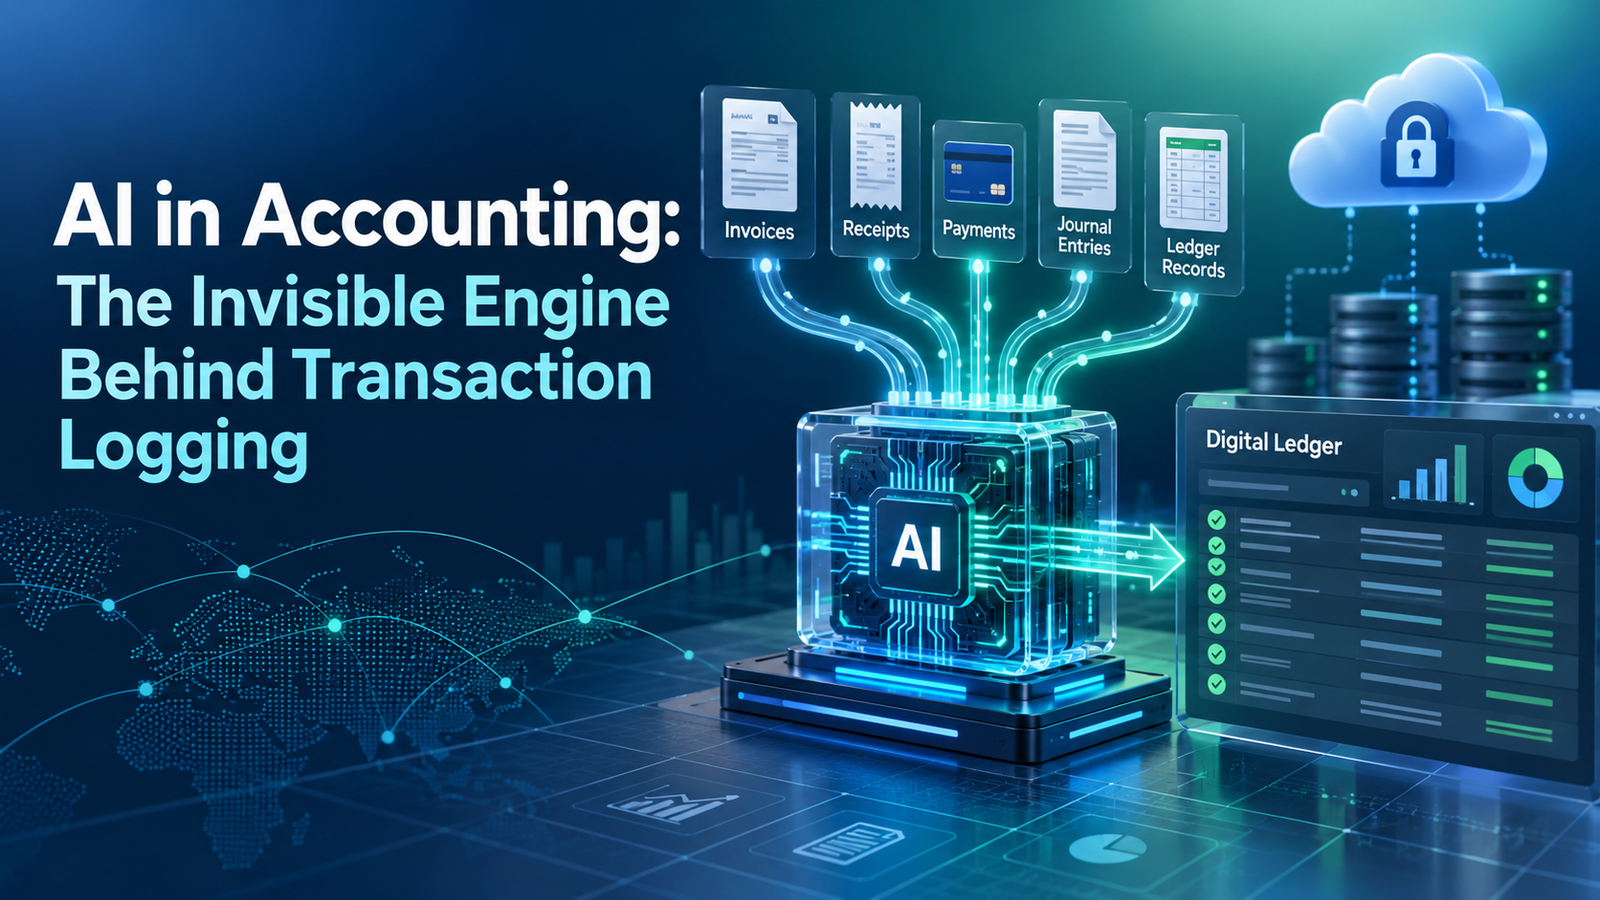
The entry point for most AI deployments is document processing — the automated extraction, validation, and posting of transactional data from invoices, receipts, bank files, and remittance advice.
This is not simply OCR. Modern document AI uses a combination of layout analysis, contextual language models, and entity recognition trained on domain-specific corpora to extract fields with reliability that now regularly exceeds 95% straight-through processing rates on structured supplier invoices. More meaningfully, these systems handle the real-world messiness that rule-based extraction never could: supplier names that don’t match master data exactly, invoice formats that change without notice, multi-currency documents with embedded exchange rates, and line-item descriptions that bear no obvious relationship to the chart of accounts.
| WORKED EXAMPLE — SUPPLIER NAME DISAMBIGUATION A £42,800 invoice arrives described as “Microsoft Azure — EMEA Cloud Services Ref: INV-2024-88341.” Your vendor master lists the supplier as “Microsoft Ireland Operations Ltd.” Your PO references “cloud infrastructure.” A rule-based system fails to match all three. The AI — having learned that these strings co-occur in your transaction history — matches them with 98% confidence, posts to the correct cost centre, and applies the correct VAT treatment without human intervention. The same invoice, processed manually, takes 4 minutes and introduces one opportunity for a keying error. Across 800 such invoices per month: 53 hours of avoidable labour and roughly 8–12 likely posting errors requiring correction at period-end. |
Continuous Reconciliation
Traditional reconciliation is periodic and sequential: bank to ledger, subledger to ledger, intercompany — typically monthly, sometimes weekly for high-volume accounts. The gap between transaction date and reconciliation date is a control gap. Errors compound. Adjustments become harder to trace.
AI-driven reconciliation operates continuously. Matching algorithms trained on your historical transaction patterns — supplier naming conventions, payment terms, typical settlement lags, intercompany structures — match the vast majority of transactions in near real-time and escalate exceptions the moment a mismatch is detected.
Table 2 — Reconciliation approach comparison
| Dimension | Traditional reconciliation | AI-driven reconciliation |
| Frequency | Monthly (weekly for key accounts) | Continuous — near real-time |
| Coverage | All items — but detected in arrears | All items — flagged within hours |
| Error detection lag | 15–30 days average | Minutes to hours |
| Fuzzy matching | Requires exact or near-exact match rules | Learns naming variations, FX patterns |
| Audit trail | Manual notes, spreadsheet history | Full decision log with confidence scores |
| Close impact | Week 1 consumed by recon cleanup | Close begins with clean, pre-reconciled data |
Table 2 — The detection lag column is the most significant control variable for audit committees to focus on.
Anomaly Detection and Fraud Pattern Recognition
Every organisation has a financial fingerprint — characteristic patterns in how transactions flow, when they occur, what they look like, and how they relate to each other. AI systems analyse that fingerprint continuously and flag deviations. Below is a representative sample of what a live monitoring system surfaces in a single day’s transactions.
Table 3 — Live AI transaction monitoring output (illustrative)
| Transaction | Vendor | Amount | Posted by | Time | AI Flag |
| INV-9821 | Apex Logistics Ltd | £14,220 | AP system | 09:14 | Matched · 99% |
| INV-9822 | Apex Logistics Ltd | £14,220 | AP system | 09:31 | DUPLICATE — review |
| EXP-4401 | T. Harrison (expenses) | £4,950 | T. Harrison | 11:08 | Matched · 97% |
| PO-7731 | Granitex Supplies | £24,800 | J. Moore | 02:17 | Off-hours · new vendor |
| PO-7732 | Granitex Supplies | £24,600 | J. Moore | 02:44 | Off-hours · new vendor |
| PO-7733 | Granitex Supplies | £24,900 | J. Moore | 03:02 | SPLIT PATTERN — escalated |
| INV-9830 | City Print Services | £1,840 | AP system | 14:22 | Matched · 96% |
Table 3 — INV-9822 is a duplicate submitted 17 minutes after INV-9821. PO-7731 through 7733 show a classic transaction-splitting pattern: three invoices from a new vendor, each below a £25,000 approval threshold, posted by the same user between 2–3am. No single transaction violates policy. The pattern does.
| WHY TRANSACTION SPLITTING EVADES TRADITIONAL CONTROLS A £25,000 approval threshold is a common control point. An employee or colluding vendor who knows this threshold can systematically split invoices to stay below it. If each invoice passes three-way matching individually, the pattern is invisible to rule-based systems. AI detects the pattern by analysing all three transactions together, noting the new vendor relationship, the after-hours timing, and the proximity to the threshold. None of those signals alone is decisive. Their combination is. |
The anomaly categories worth understanding:
- Statistical outliers — Transactions that fall outside the expected distribution for a vendor, cost centre, or account. These surface legitimate errors as readily as fraud.
- Behavioural anomalies — Changes in user behaviour: transactions posted outside business hours, a spike in manual journal entries from a single source, approval workflows suggesting rubberstamping.
- Network-level signals — Relationships between vendors, bank accounts, employees, and transactions that individually look clean but collectively suggest collusion or ghost vendor schemes. This is largely invisible to traditional controls.
- Policy drift — Transactions that comply with policy technically but represent systematic drift: expense catch-alls, PO limits gamed through splitting, approval thresholds approached but never crossed.
Table 4 — Anomaly typology by financial risk and detection complexity
| Duplicate Invoices Risk level: Low · Detection: Simple • 0.1–0.5% of payments • Simple to detect with AI • Often accidental, sometimes deliberate • Caught by periodic recon — too late | Policy Drift Risk level: Low–Med · Detection: Complex • Threshold gaming (e.g. split invoices) • Expense catch-all misuse • Requires pattern analysis across time • Often missed until audit |
| Mispostings & Keying Errors Risk level: High · Detection: Simple • Wrong account codes • Wrong period postings • ICFR risk if material • AI detects at capture, not period-end | Ghost Vendors & Collusion Risk level: High · Detection: Complex • Network graph analysis required • Individually clean transactions • Collectively fraudulent • Invisible to traditional sampling controls |
Table 4 — Traditional controls catch duplicates (top-left) reasonably well. Mispostings (bottom-left) are caught at reconciliation, but in arrears. Policy drift and ghost vendor schemes (right column) are largely invisible without AI-driven pattern analysis across the full transaction population.
The ROI Conversation
Finance leaders evaluating AI investment will encounter vendor claims that are, charitably, optimistic. A more grounded framework focuses on three categories of return:
- Hard efficiency gains — Reduction in manual processing time for data entry, matching, and reconciliation is real and typically the fastest to realise. Time-to-close reductions of 25–40% are achievable and documented.
- Error and loss reduction — Duplicate payment detection alone often delivers positive ROI within the first year. Industry estimates suggest 0.1–0.5% of B2B invoice payments are duplicates.
- Control value — AI-driven monitoring covers 100% of transactions continuously — compared to periodic sampling that covers a fraction of the population in arrears.
| WORKED EXAMPLE — DUPLICATE PAYMENT RECOVERY A professional services firm processing £180M in annual supplier payments deploys AI-driven duplicate detection. At a 0.2% duplicate rate — conservative by industry standards — that represents £360,000 in payments made twice per year. The AI flags duplicates before payment where possible; where payment has already occurred, it triggers vendor recovery requests within 48 hours rather than surfacing through quarterly statement reconciliation. Year 1: £290,000 recovered. Licensing and implementation: £85,000. Net gain from this single detection category alone: £205,000 — before efficiency gains, error reduction, or audit savings. |
Table 5 — Illustrative Year 1 ROI breakdown (mid-market professional services firm, £180M annual payments)
| Item | Amount (Year 1) | Category |
| Implementation | £85,000 | Cost |
| Annual licence (Yr 1) | £42,000 | Cost |
| Change management | £30,000 | Cost |
| Total cost | £157,000 | |
| Duplicate payment recovery | £290,000 | Return |
| Labour savings (2 FTE redeployed) | £180,000 | Return |
| Error correction savings | £65,000 | Return |
| Total return | £535,000 | |
| NET YEAR 1 GAIN | £378,000 | Net |
| ROI on total cost | 3.4× | Net |
Table 5 — Figures are indicative. Actual returns vary by transaction volume, duplicate rate, and process maturity. The labour saving estimate assumes 2 FTE redeployed from AP data entry to exception review and analysis.
The cost side includes licensing, implementation, ERP integration, ongoing model governance, and the change management required to redesign workflows. Organisations that underinvest in the last two items consistently underperform on the first three.
Adoption Maturity: Where Most Organisations Stand
Understanding where your organisation sits on the AI adoption curve is a prerequisite for prioritising investment. The four-stage model below reflects current enterprise adoption patterns across the finance function.
Table 6 — AI in accounting: four-stage maturity model
| Stage 1 Document AI Invoice OCR GL auto-coding STP >90% Most orgs here | Stage 2 Reconciliation AI Bank reconciliation Fuzzy matching Real-time close ~40% of enterprises | Stage 3 Anomaly Detection Fraud signals Behavioural analysis Network graphs ~15% of enterprises | Stage 4 Predictive Finance Cash flow forecast Variance explanation Audit-ready output <5% of enterprises |
Table 6 — Most mid-market and enterprise organisations have reached Stage 1–2. Stage 3 (anomaly detection at scale) is the highest-value investment available to controllers today. Stage 4 remains nascent but is advancing rapidly in ERP roadmaps from SAP, Oracle, and Workday.
The common stall point between Stage 2 and Stage 3 is not technology — it is governance. Organisations that have clean document AI and functional reconciliation automation stall at anomaly detection because they have not established the model governance framework required to deploy and validate continuous monitoring tools with confidence.
What Controllers and Audit Committees Need to Get Right
Model Governance Is Now a Finance Responsibility
When AI makes a posting decision, approves a match, or flags an anomaly, it is exercising a form of judgment that sits inside your control framework. That model needs to be governed with the same rigour you would apply to any other control.
| THE GOVERNANCE GAP MOST FINANCE TEAMS ARE MISSING Many finance teams are deploying AI tools whose governance sits entirely in IT or with a vendor. That is a control gap. The controller who cannot explain to an auditor how the AI made a classification decision has the same problem as the controller who cannot explain how a human made it. When your external auditor asks “how was this transaction classified?”, “the system did it” is not an acceptable answer — and increasingly, it is not one auditors will accept. |
Table 7 — AI model governance lifecycle for finance teams
| 1. Design & Scope Define use cases Ownership & RACI Risk thresholds | 2. Train & Validate Clean training data Accuracy benchmarks Explainability review | 3. Deploy & Monitor Confidence thresholds Drift alerts Exception logging | 4. Review & Audit Periodic testing External audit input Finance owns this | 5. Retrain & Update Fraud remediation Data cleansing Model versioning |
Table 7 — The governance cycle should run continuously. Review & Audit should run quarterly at minimum. Retrain should be triggered whenever model accuracy drops below agreed thresholds or the transaction environment changes materially (ERP migration, M&A, new business lines).
Training Data Quality Determines Output Quality
For organisations deploying out-of-the-box AI from ERP vendors or specialist fintech providers, the relevant question is: was this model trained on transaction data that resembles your organisation’s environment? Industry composition, transaction structure, vendor geography, and chart of accounts design all affect model performance.
| THE TRAINING DATA TRAP An AI model trained on a ledger that contains historical fraud may learn to treat that fraud as normal. If your transaction history includes three years of a ghost vendor scheme that was only discovered last quarter, a model fine-tuned on that history may classify future similar transactions as legitimate. This is not a theoretical concern. It is a specific validation question your model governance process should require an answer to before go-live. |
Human Review Remains a Control, Not a Formality
Straight-through processing rates of 95% or higher sound impressive. But the 5% of transactions that fall outside AI confidence thresholds are, by definition, the most complex, unusual, and high-risk items in the population. If the humans reviewing that queue are doing so under time pressure with inadequate context, the efficiency gain has come at the cost of control quality on exactly the transactions that most warrant scrutiny.
| THE RIGHT DESIGN AI handles high-confidence, routine transactions without human intervention. Everything below threshold routes to reviewers with the AI’s reasoning, relevant context (matching history, vendor profile, applicable policy), and a clear escalation path. The reviewer’s job is not to ratify the AI’s work — it is to exercise judgment where the AI has flagged that judgment is required. Measuring reviewer throughput in this queue as a performance metric is a mistake; it incentivises the wrong behaviour. |
The Audit Committee Lens
For audit committee members, AI in the transaction layer creates both opportunity and new oversight responsibility. The opportunity is genuine: continuous coverage, faster anomaly detection, and consistent control application are improvements over any sampling-based approach.
The new responsibility: AI systems influencing the financial close and reporting process are now part of the ICFR framework. Committees that are not asking about model governance, training data quality, and AI-specific control design are leaving a gap in their oversight.
Table 8 — Practical questions for audit committees to raise with management and internal audit
| 1 | Which AI systems are making or influencing posting decisions in our financial systems? Many finance teams cannot answer this completely. ERP vendors have been embedding AI capabilities without explicit disclosure. The inventory itself is a necessary first step. |
| 2 | How are those systems validated, and how frequently? Model performance degrades as your transaction environment evolves. A model validated at deployment may be significantly less accurate 18 months later. Validation frequency and methodology should be documented. |
| 3 | What is our process when an AI model’s performance degrades or its outputs are found to be systematically incorrect? This is the business continuity question for AI controls. The answer should not be “we would notice through other controls” — that defeats the purpose of having AI controls in the first place. |
| 4 | Has external audit reviewed the control design around AI-assisted processes? External auditors are increasingly including AI systems in ICFR scope. Confirm whether the current methodology addresses AI-assisted controls or relies on pre-AI assumptions. |
Conclusion: Directing the Engine
AI is not coming to the transaction layer. For most organisations, it is already there — embedded in ERP systems, payment platforms, banking infrastructure, and specialist accounting tools that have been quietly adding machine learning capabilities for years.
The finance leaders who will extract the most value are not those who deploy AI aggressively for its own sake. They are those who deploy it with a clear understanding of where AI judgment is reliable, where human judgment remains essential, and how to build a governance framework that treats AI-assisted controls with the same rigour as any other control.
The transaction layer is the foundation of financial truth in your organisation. The engine running it is increasingly invisible. Making sure you understand it — and direct it — is not optional.
References
The following sources informed the data, benchmarks, and frameworks cited in this article. Industry statistics are indicative; organisations should validate figures against their own transaction profiles and current vendor documentation.
- Association of Certified Fraud Examiners (ACFE). Report to the Nations: Global Study on Occupational Fraud and Abuse. ACFE, 2024. Available at: acfe.com/report-to-the-nations
- Ardent Partners. Accounts Payable Metrics That Matter in 2024. Boston, MA: Ardent Partners. (Source for duplicate payment rate estimates of 0.1–0.5%.)
- Gartner. Magic Quadrant for Accounts Payable Invoice Automation Solutions, 2024. Gartner, Inc.
- McKinsey Global Institute. The Age of AI: And Our Human Future. McKinsey & Company, 2024.
- Deloitte. AI in Internal Audit: Navigating New Frontiers. Deloitte Insights, 2024.
- PwC. Global Economic Crime and Fraud Survey 2024. PricewaterhouseCoopers International, 2024.
- Institute of Internal Auditors (IIA). Artificial Intelligence Auditing Framework: Practical Applications. IIA Research Foundation, 2024.
- SAP SE. SAP S/4HANA Finance: AI-Powered Financial Close Documentation. SAP Help Portal, 2024.
- Oracle Corporation. Oracle Fusion Cloud ERP: AI for Finance Overview. Oracle Documentation Library, 2024.
- Workday, Inc. Workday Financial Management: Machine Learning Capabilities. Workday Documentation, 2024.
- International Auditing and Assurance Standards Board (IAASB). Proposed International Standard on Auditing for Audits of Financial Statements of Less Complex Entities. IFAC, 2024.
- COSO (Committee of Sponsoring Organizations of the Treadway Commission). Internal Control — Integrated Framework: Considerations for AI-Enabled Internal Controls. COSO, 2024.
- AppZen. The State of AI in Finance: 2024 Benchmark Report. AppZen Inc., 2024.
- Medius. AP Automation Benchmark Report: Straight-Through Processing Rates Across Industries. Medius, 2024.
- European Commission. EU AI Act: Implications for Financial Services Organisations. Official Journal of the European Union, 2024.
